Status of this post: COD 3.8.5, November 2026. Later versions may differ. For the current feature status see the roadmap.
Many organisations ask where they stand with NIS2. The answer is rarely in a single document. It is spread over risk analysis, policies, supplier contracts and the knowledge of individual people. The Statement of Applicability, SoA for short, brings it together. For every requirement it says whether it applies, how far it is implemented and which document supports that.
In the COD demo you can see this in five minutes. Sign in with the account Demo GRC. The access details are on extocode.com/demo. The data belongs to a fictional industrial company, Kesselbach Antriebstechnik GmbH. The figures below are the state of 4 November 2026 on COD 3.8.
Minute 1: Risks at a glance
The GRC dashboard starts with the risk matrix. One axis shows the damage, from "low" to "catastrophic". The other shows the probability, from "very rare, less often than every ten years" to "frequent, several times a year". Each cell shows how many assessments sit there.
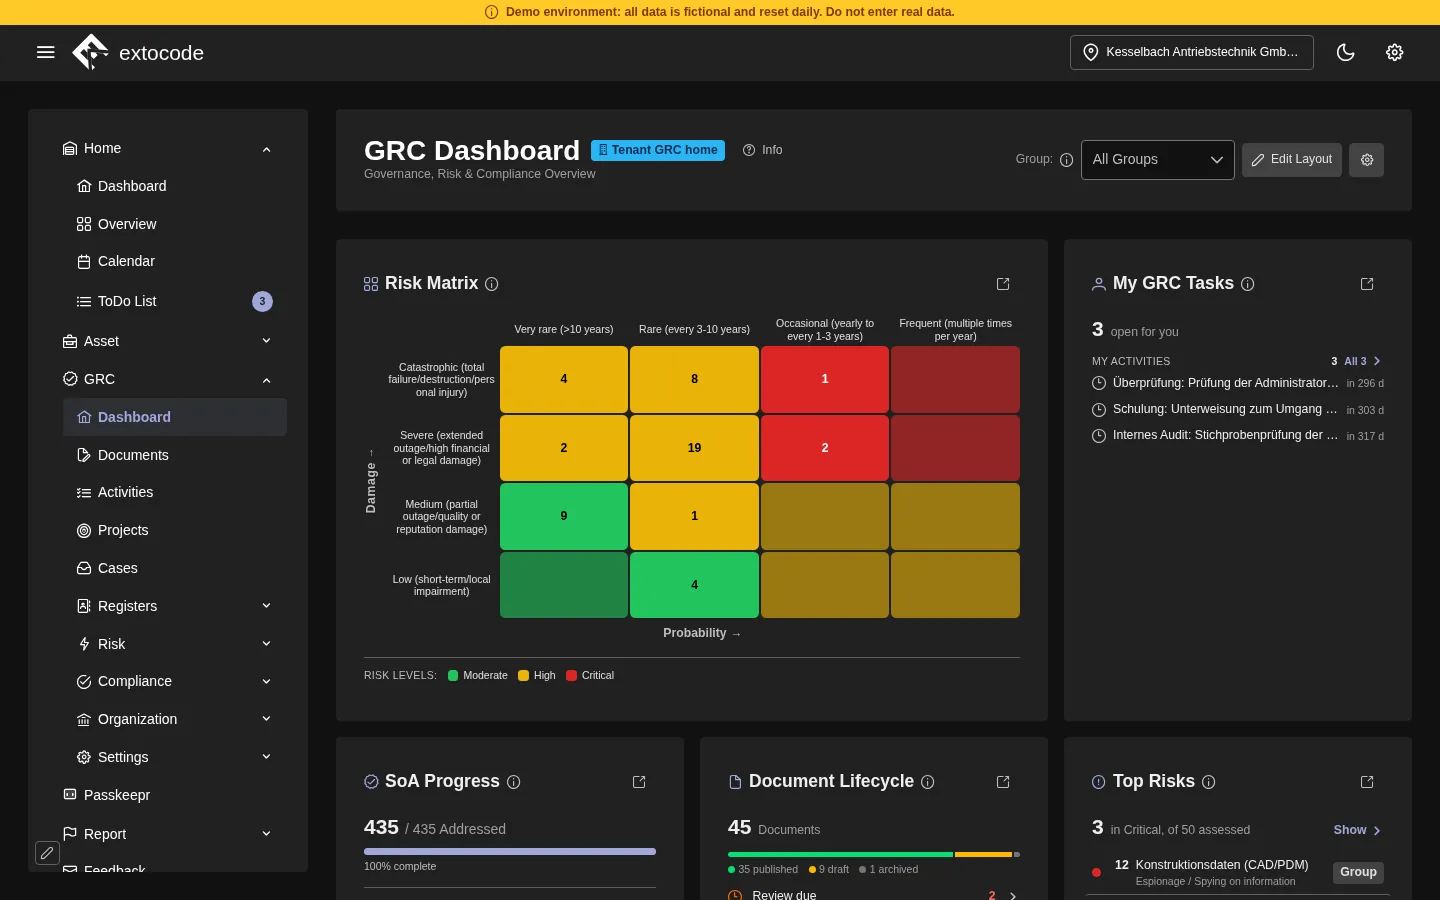
Kesselbach has 50 risk assessments, 3 of them in the critical range. At the top is espionage on the design data from the CAD and PDM system. Next to it the dashboard shows the state of the documents: 45 documents, of which 35 are published, 9 are drafts and 1 is archived. Two reviews are overdue.
Minute 2: Six catalogues in one view
Under Compliance, open the Statement of Applicability. The default is "Global - All Norms". The view merges the catalogues Kesselbach uses:
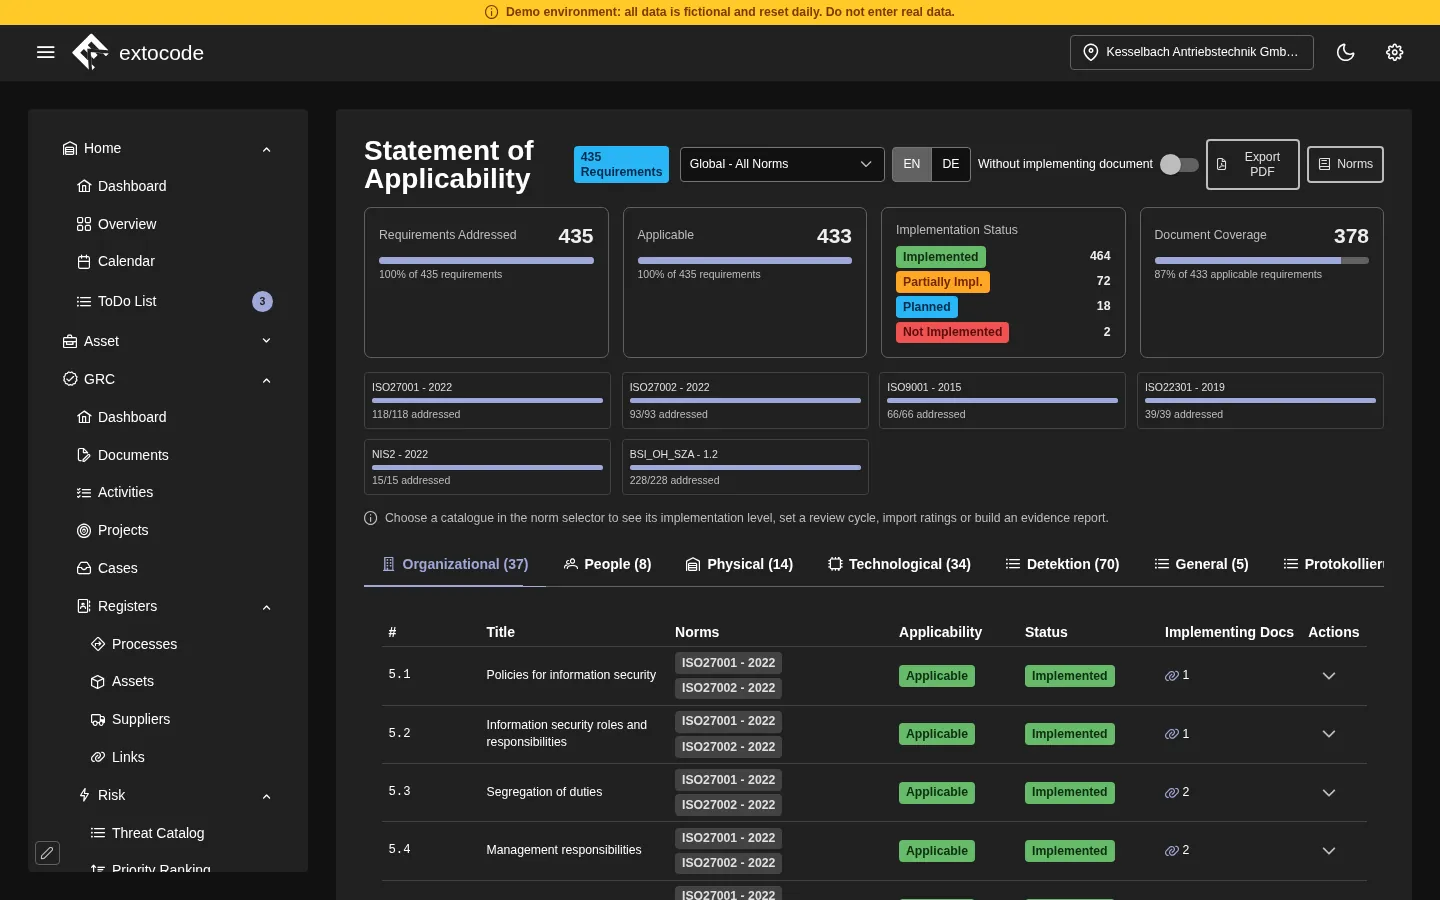
- ISO/IEC 27001:2022 with 118 requirements
- ISO/IEC 27002:2022 with 93
- ISO 9001:2015 with 66
- ISO 22301:2019 with 39
- NIS2 with 15
- BSI guidance on the use of systems for attack detection (Orientierungshilfe zum Einsatz von Systemen zur Angriffserkennung, version 1.1 of 18 November 2024, in COD as BSI OH SzA) with 228
In COD the catalogue is called BSI_OH_SZA 1.2. The 1.2 is the version of the BSI requirement texts that COD adopts.
Together that is 559 requirements across the catalogues. Where norms overlap, there is one row, with both norms as tags. The global view counts 435 rows that way. 433 of them apply to Kesselbach.
The important part is to keep two questions apart. Does a requirement apply? And is its implementation documented? At Kesselbach, 378 of 433 applicable requirements have an implementing document. That is 87 percent. The switch "Without implementing document" shows the other 55. With "EN" and "DE" you switch the requirement texts between English and German. The texts are paraphrased and are not the wording of the norms.
Minute 3: NIS2 on its own
Choose "NIS2 - 2022" in the norm field at the top. The view shrinks to 15 requirements in three areas:
- Governance with 2 requirements from Article 20, such as approval of the measures by management and their training
- Cybersecurity risk-management measures with 10 requirements from Article 21
- Reporting obligations with 3 requirements from Article 23
At Kesselbach, 12 of these requirements are entered as "Implemented" and 3 as "Partially Impl.". Those are supply chain security, multi-factor authentication and the early warning to the competent body. Every requirement has at least one implementing document.
Above that, the card "Implementation level" shows a level for the catalogue and for each area. COD works it out itself from the entries. Level 0 means nothing has been started. Level 1: only planned. Level 2: started. Level 3: all must-requirements of the area are fulfilled. The level of the catalogue is the lowest of the areas. At Kesselbach, Governance is at 3. The other two areas are at 2 and limit the overall value. COD says so on the card.
Two notes on the level. The card shows it as "2 / 5", but COD computes only levels 0 to 3. You set levels 4 and 5 by hand only, with a reason. And the level describes the state of your documentation. It does not say whether an organisation meets NIS2.
In the table you also see the column "Last review". At Kesselbach it reads "Never reviewed". If you set a review cycle, COD creates an activity 30 days before the date.
Minute 4: Suppliers and their evidence
NIS2 also speaks about security in the supply chain. Open Suppliers. For each supplier you see which service it provides, how critical it is and which evidence it owes: a questionnaire, a supplier audit or a certificate. How much is required depends on the level of the supplier. For suppliers at the middle level, COD asks for no evidence.
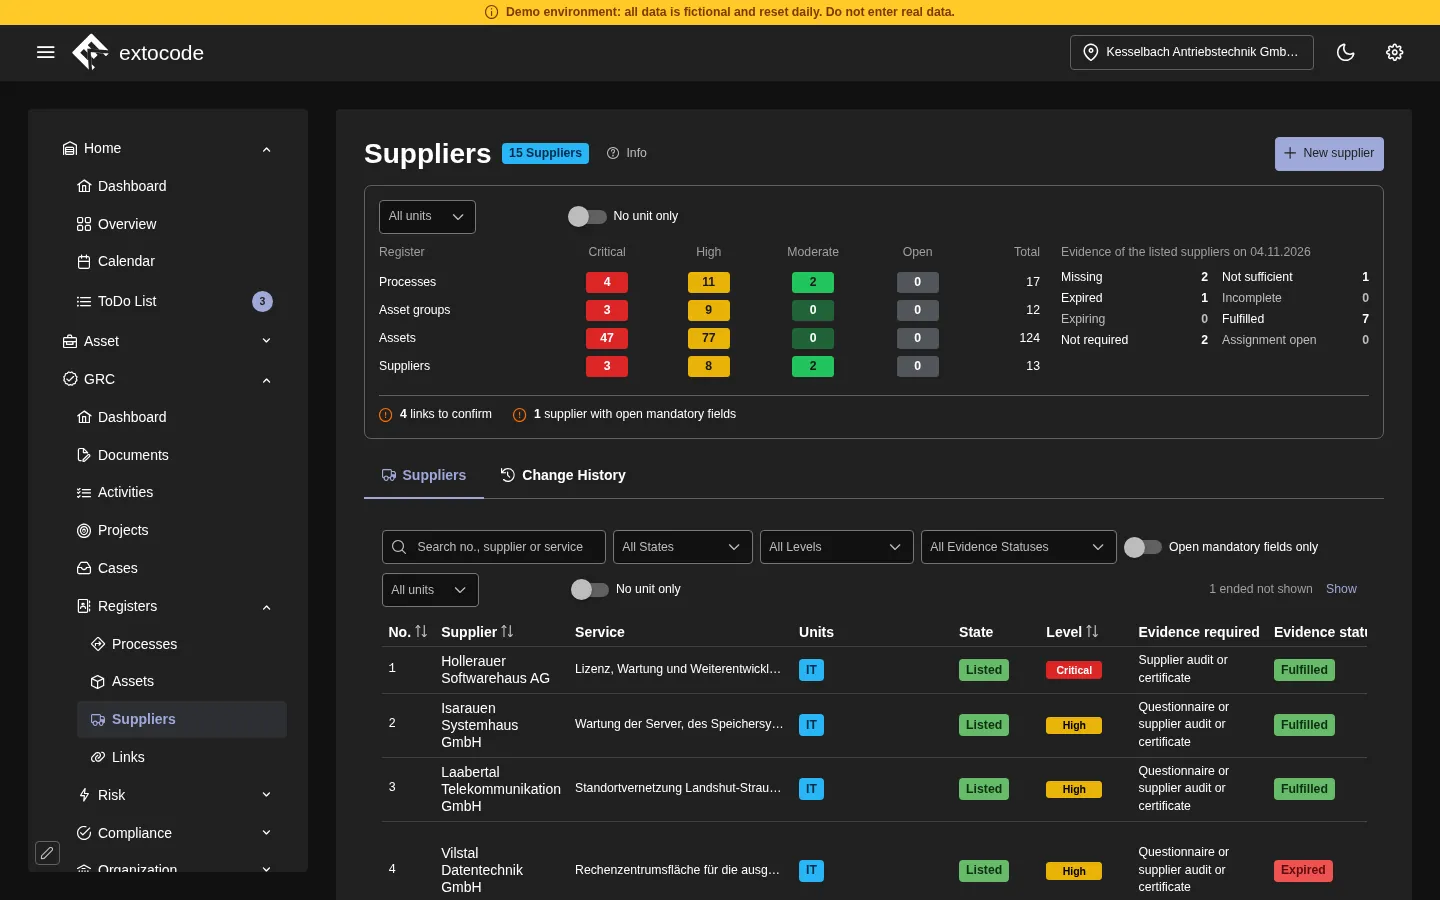
The overview at the top counts for 13 suppliers: 7 fulfilled, 2 not required, 2 missing, 1 not sufficient and 1 expired. The expired evidence belongs to the supplier that provides the data centre space for the outsourced backup tapes. It was valid until 24 June 2026. The column "Next step" says what to do now: request the questionnaire, the audit or the certificate.
In the demo, the SoA requirement on supply chain security is at "Partially Impl.". On the supplier page, four suppliers have open evidence. You see both side by side, in the same account.
Minute 5: What comes of it
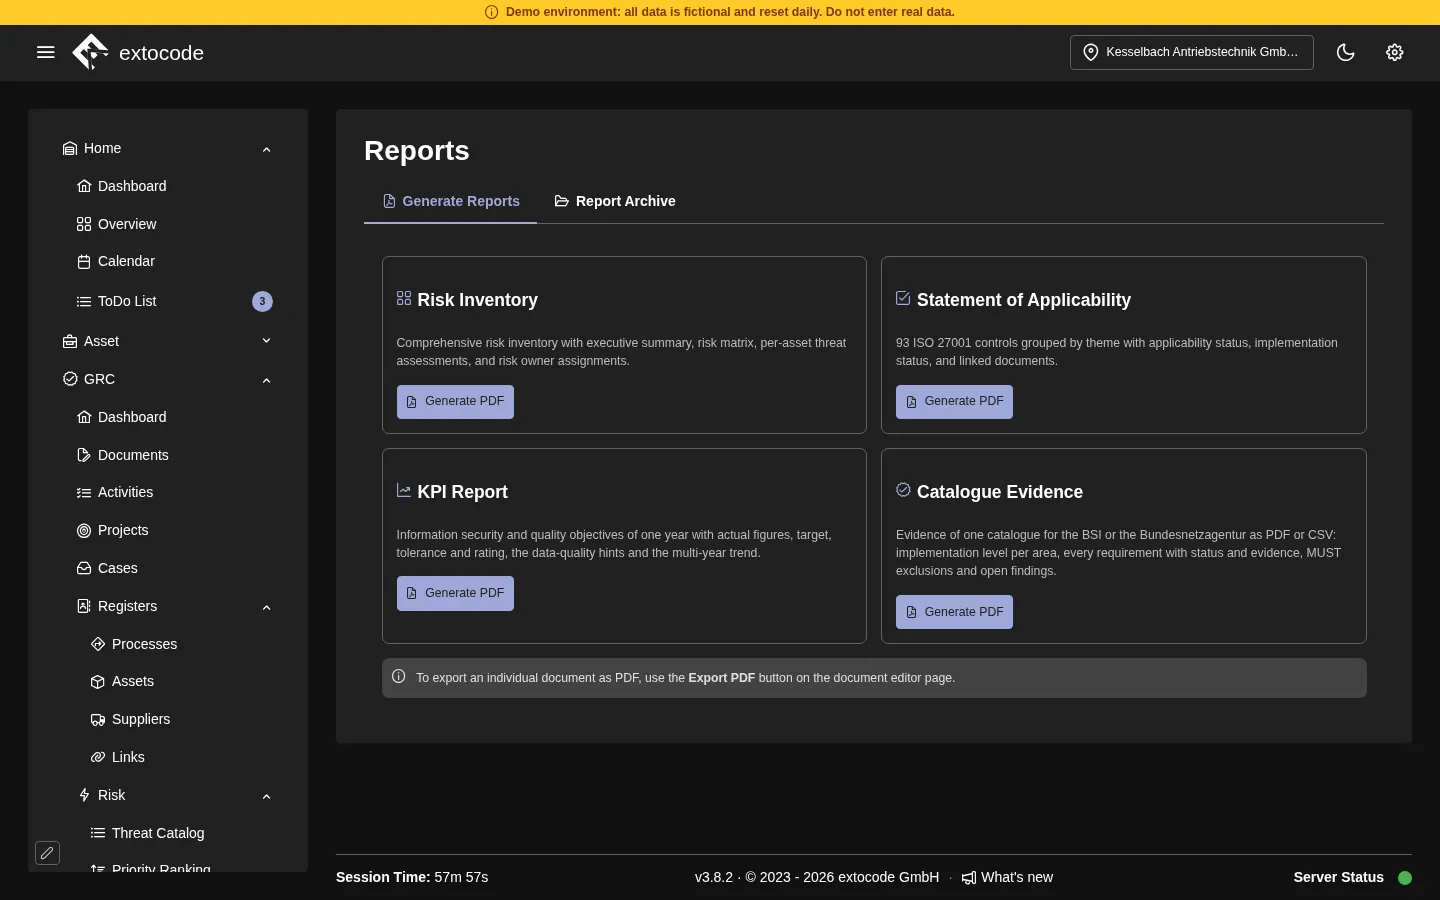
Under Reports you find the reports needed for audit and management: the risk inventory, the Statement of Applicability, a KPI report and the evidence of a catalogue for the BSI or the Bundesnetzagentur, as PDF or CSV. Under Cases you find findings, reports and incidents with status, severity, responsible person and due date.
What COD does for NIS2
COD does not make an organisation compliant with NIS2 and does not replace legal advice. COD helps with preparation (readiness): it maps the requirements, links them to risks, documents and suppliers, and helps you document where you stand. In the demo, the risk assessments hang on asset groups such as "Network and firewalls data centre" or "ERP system", each with its assets. Whether your measures are enough is for you and your advisers to judge.
Which functions your contract covers follows solely from the service description in the version that applies to your contract.
See it yourself or have it shown
- Demo with the account Demo GRC: cod.demo.extocode.com, access details on extocode.com/demo
- Personal walkthrough with your questions on NIS2, ISO 27001 or ISO 22301: extocode.com/demo
extocode GmbH · Central Operations Dashboard