<COD>
Central Operations Dashboard
One dashboard. Every vendor. Full control.
"NIS 2 doesn't fail on technology.
It fails on chaos."Your entire IT and OT. Centrally managed, on-premises, provably secure.
Trusted by critical infrastructure operators
Deployed where downtime is not an option
Many of our customers are KRITIS operators. For confidentiality reasons we don't name names, but COD runs in daily operation at organizations for which downtime and data loss are not an option.
In real-world use
2.5M+
monitored sensors
Thousands
managed switches
IT + OT
devices via a central NAC
You know these problems. COD solves them.
Not another tool with feature lists, but answers to the situations that really slow down your IT day-to-day.
Vendor lock-in
“Once it is in place, we will never get rid of that tool again.”
Not with us.
If you wish, COD runs entirely in your own infrastructure and uses open standards such as SNMP, SSH, 802.1X, and TACACS+. If we run COD for you, you receive your data on request in a common format.
Integrations →Too many vendors and tools
“A separate management tool and a separate login for every vendor.”
We solve that.
COD discovers network devices from nine vendors and manages firewalls from four vendors in one interface. All modules work on one shared asset base.
All modules →Documentation chaos
“Our documentation is scattered, outdated, or stuck in a few people's heads.”
COD collects automatically. InfoScan drafts the texts.
COD discovers ports, VLANs, clients, addresses, and routes by itself and draws the topology. The InfoScan add-on uses local AI to draft your system documentation. You decide what gets adopted.
Network & Assets →No overview of the standards
“ISO 27001, ISO 9001, NIS2: we maintain a separate silo for every standard.”
We clean it up and deliver GRC.
GRC keeps ISO/IEC 27001, ISO 9001, ISO 22301, and NIS2 in one catalog and folds overlapping requirements into one row. GRC does not replace certification. It prepares your evidence.
GRC & Compliance →Open network access
“Every unused network jack is an open door.”
Access only with authorization.
COD-NAC enforces access control with 802.1X and MAC addresses, using its own PKI. Time-limited approvals expire by themselves.
NAC & PKI →Unclear admin rights
“Who may run which commands on which switch? Nobody knows for sure.”
Command rights in one place.
The included TACACS+ server manages users, devices, rules, and roles, with accounting. A simulator shows in advance whether a command would be allowed.
TACACS+ →Scattered passwords
“Team passwords live in notes, chats and someone else's cloud.”
Shared, but encrypted.
Stronghold stores passwords and secrets with end-to-end encryption, in personal and shared vaults. The server stores only ciphertext.
Stronghold →Lost configurations
“If a device configuration is lost, we reconstruct it from memory.”
Backed up and comparable.
COD backs up configurations across vendors and on a schedule. You see the differences between two versions down to the single file.
Backup →Plus monitoring with Zabbix, network and assets, guest access via captive portal, VMware networks, and rolling out configurations across entire port ranges with automation. All problems in detail →
Which of these problems hits you hardest?
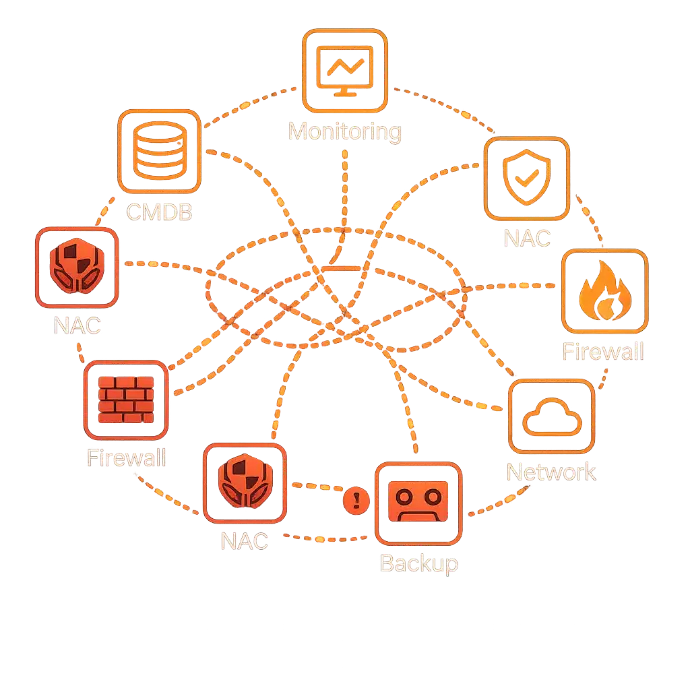
The real problem
Your IT doesn't know itself.
- The information exists,
- but not centrally,
- not connected,
- not reusable.
The turning point
- Capture once.
- Use everywhere.
- No more rethinking it for every topic.
- Instead, build one shared foundation.
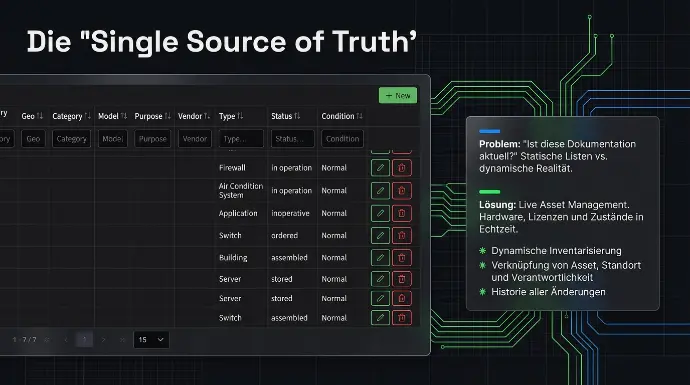
How order takes shape
- One source for all information
-> Assets, systems, networks, set up cleanly once.
- Everything builds on it automatically
-> NIS 2, GRC, risks, evidence.
- Changes take effect everywhere
->No duplicate upkeep. No inconsistencies.
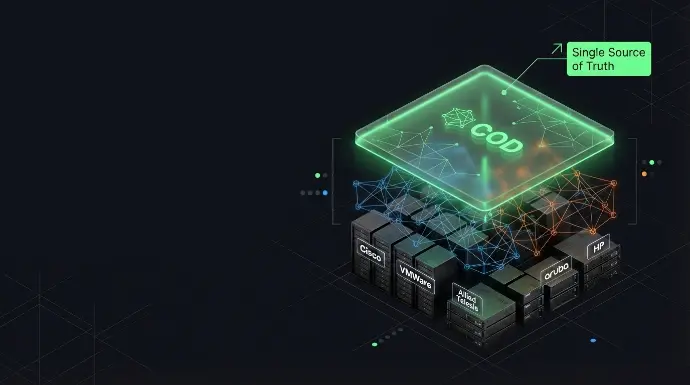
The result
- Less effort.
- More oversight.
- Provable security.
- NIS 2 becomes a by-product, not a never-ending project.
Why operators in regulated industries trust COD
With COD, security, auditability, and data sovereignty aren't add-ons, they're the foundation.
On-premises, full data sovereignty
No forced cloud. COD runs entirely in your data center and is KRITIS-ready. Your data never leaves the building.
NIS2 & ISO in view
The GRC module covers ISO 27001, ISO 9001, ISO 22301, and BSI 200-3, on live asset data instead of outdated lists.
Protected GRC audit log
GRC logs changes field by field. The log is append-only, and a database trigger protects it against changes and deletion.
Vendor-independent
No vendor lock-in. Firewalls and switches from different vendors and your VMware environment come together in a single interface.
Made in Germany
Development and support from Traunstein, Germany. A single German point of contact and German data-protection standards.
Multi-tenant & GDPR-compliant
Customers, sites, and departments cleanly separated, role-based via LDAP/AD, and operable in full GDPR compliance.
What operators report
Voices from daily operation, anonymized for confidentiality.
"Every open network port was an open door. Unknown devices no longer just walk onto the production network."
"On-premises was a requirement for us, not a nice-to-have. Our credentials don't sit in someone else's cloud."
"A lost phone used to mean a ticket escalating all the way to the developers. Now the helpdesk resets the second factor with one click."
"The guest Wi-Fi password used to be stuck to the reception desk. Now reception creates the access itself, with no firewall rights at all."
"48 ports used to mean 48 times the manual work. Now a single command rolls out the whole port range."
"We used to create every port group on each host individually. Now the rollout runs across all hosts in one go."
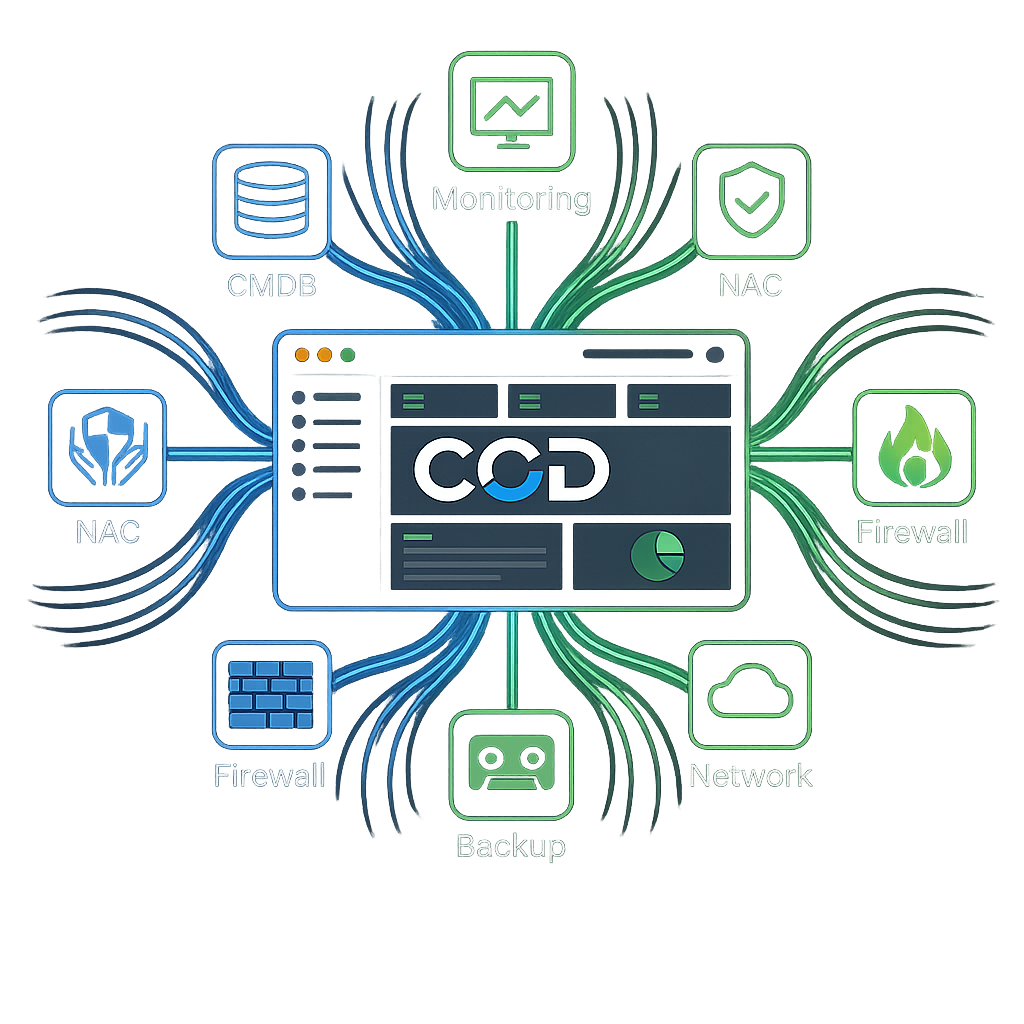
The solution
Central Operations Dashboard
The platform that cuts complexity.
One central foundation
for structure, oversight, and compliance.
👉 In short:
Chaos costs time.
Order creates security.
Why COD?
Three reasons why operators rely on COD.
Efficiency
One central entry point. Less admin effort thanks to bundled tools.
Security
Full transparency through NAC, TACACS+, and the VAS add-on.
Independence
No vendor lock-in. Freedom to choose your hardware.